MCP Integration Testing
How to Test an MCP Issue-Tracker Integration Before Live Tickets
Use a disposable issue project to verify MCP tool discovery, schemas, ticket context, writes, permission failures, and host approval behavior before enabling a coding agent on live customer work.
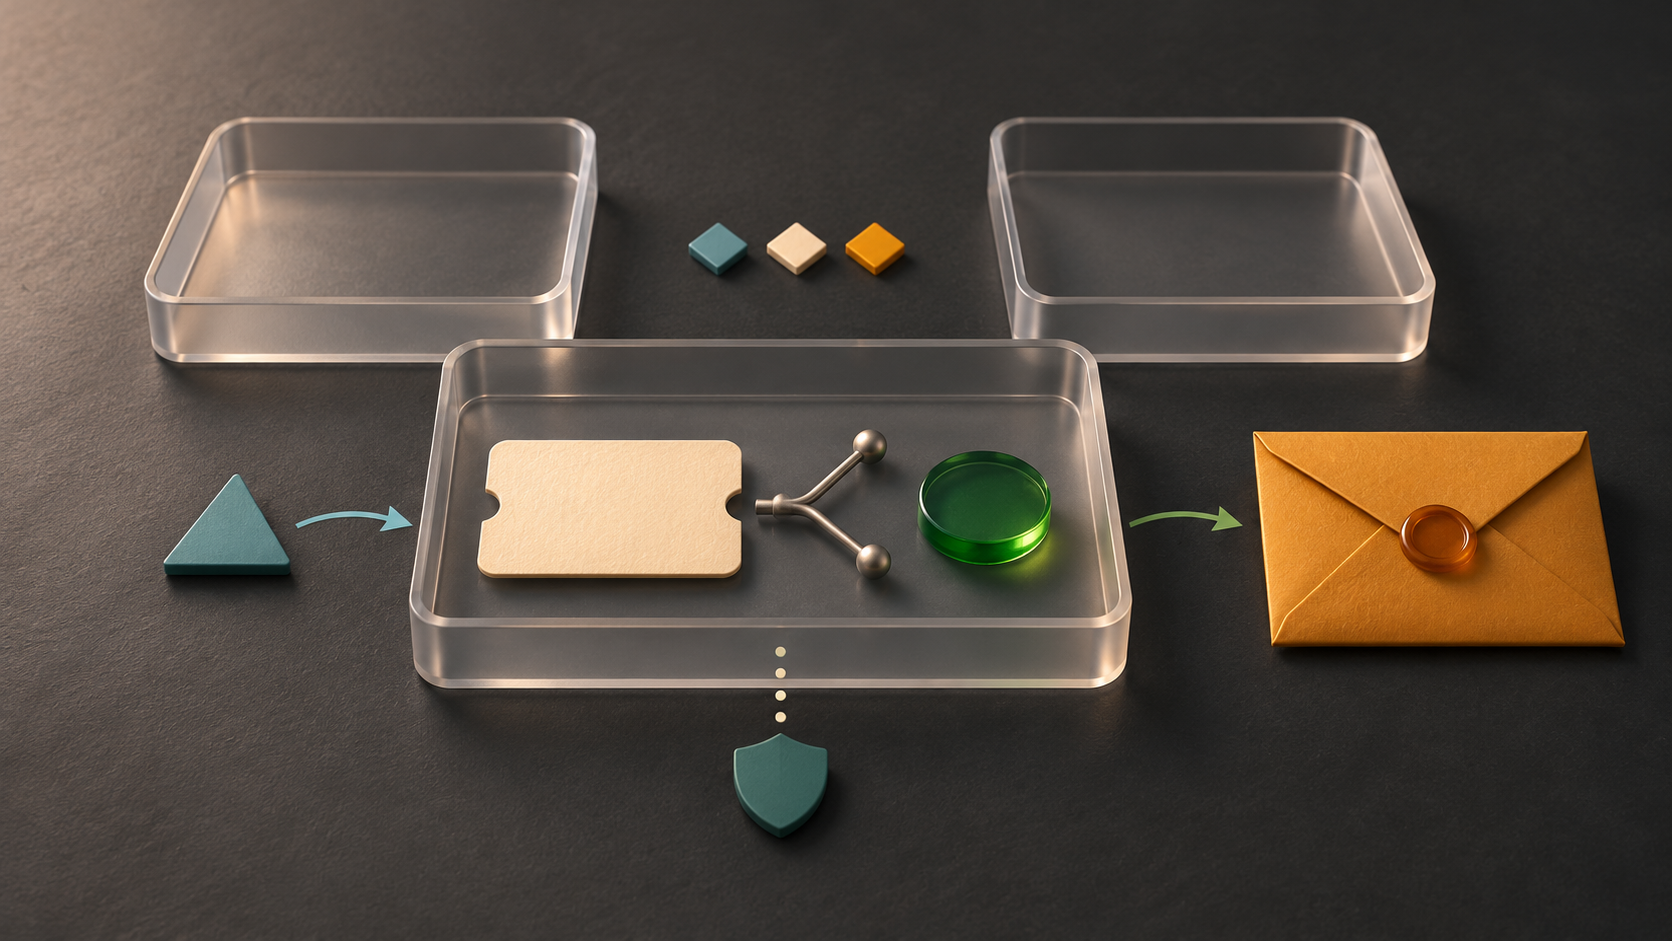
A server that starts cleanly can still expose the wrong tools, reject the arguments an agent sends, or return an issue update the model cannot interpret. Test those behaviors with a dedicated sandbox project and synthetic tickets before giving a coding agent access to live customer work.
An MCP issue-tracker integration is ready for a limited pilot when the client discovers the intended tools, valid inputs produce the expected ticket data, invalid inputs fail clearly, and write operations affect only disposable records. Treat the release as an acceptance test: capture the tool catalog, exercise representative calls through the actual client, and verify the resulting state in the tracker.
Build a fixture the team can reset
Create a separate test project or tenant with no real customer records. Add a small, documented fixture set: one ordinary bug, one report with a screenshot, one ticket with a linked code change, and one record the test account cannot access. Give every record an unmistakable prefix such as MCP-TEST-. Keep credentials scoped to this environment and remove them from the production agent configuration.
A fixture needs expected answers, not just sample rows. For the bug ticket, record the expected title, status, assignee, reporter-safe summary, and attachment count. If an agent searches for “CSV export drops the final row,” the assertion should check that the returned ticket ID and core fields match the fixture. It should not require an exact model-written paragraph, which can vary while preserving the correct facts.
An MCP acceptance fixture is a disposable dataset with known answers and permitted actions. Each fixture record should have an expected read result, a set of allowed changes, and a reset procedure. This lets a developer distinguish a server defect from a model’s wording choice.
Gate 1: compare discovery with the intended contract
First connect through the same host and transport planned for the pilot. Inspect the tools returned by tools/list: names, descriptions, required and optional arguments, enum values, and input schemas. Record the catalog as a versioned test artifact. A coding agent cannot call a tool that the host did not discover, and an ambiguous description can lead the model to select a neighboring operation.
The current MCP tools specification defines a tool’s name, description, input schema, and optional output schema. It also says clients should treat tool behavior annotations as untrusted unless they come from a trusted server. Compare the discovered catalog with your intended contract rather than assuming a “read only” label is an enforcement boundary. MCP tools specification, 2026-07-28
For each tool you expect to use, make one valid call and a few invalid calls. For example, test a known ticket ID, an empty ID if the schema requires one, a malformed ID, and an unsupported status value. Verify that rejected arguments do not reach the tracker’s mutation layer. When a tool defines an output schema, validate successful structured results against it as well. A result that says “updated” but omits the ticket identifier may be technically successful and still leave an agent without evidence to continue.
Keep transport tests separate from contract tests. A connection timeout, failed authentication, unknown tool name, and valid call with a missing required argument point to different layers. Log which layer failed so the team does not “fix” the prompt for a server or credential problem.
Gate 2: verify the meaning of returned ticket data
A schema can be valid while the content is misleading. Ask the client to retrieve each fixture and compare stable fields: ticket ID, title, current status, project, assignee, linked pull request or commit, and whether an attachment is present. If the tool returns conversation history, confirm the order and authorship of messages. If it returns a screenshot or attachment link, check that the client handles the content type and access failure without inventing what the image contains.
Then run a short agent-level scenario. Ask the coding agent to summarize the fixture and identify the next debugging step. A reviewer should check whether the summary preserves the ticket’s observed facts, labels hypotheses as hypotheses, and names missing evidence. Keep this review distinct from server correctness: the server test checks what data arrived; the model evaluation checks what the agent concluded from it.
MCP tool results can contain text, images, audio, resource links, embedded resources, or structured content. The client must pass the result through in a form the host can actually consume, and a declared output schema should match the structured result. MCP tools specification
Gate 3: exercise writes only against disposable records
Read access rarely reveals the hardest integration bugs. For each write action, define the intended state transition before making the call. A status change should begin at a known status and end at an expected status. An assignment test should set a synthetic user and verify the resulting assignee. A comment test should add a marked test comment and then retrieve it. A link-to-commit test should verify the exact synthetic commit URL.
A useful write assertion has four parts: initial state, requested action, expected final state, and cleanup. Capture the server result and independently read the issue afterward. This catches the case where a tool returns success while the tracker rejects or normalizes the change differently than expected. Include a repeat call to determine whether the operation duplicates a comment, fails safely, or behaves idempotently. Do not assume retries are harmless.
For actions that combine a customer issue and repository context, keep the test repository harmless too. Use a throwaway branch and a synthetic commit; never use a customer ticket as a convenient test case. If your workflow needs a human approval step for comments or status changes, verify that approval in the host application. The MCP protocol leaves the user interaction pattern to the implementation, while its security guidance recommends confirmation for sensitive actions. MCP tools specification
Gate 4: prove the boundaries fail closed
Acceptance tests should include the calls a well-behaved agent must not complete. Try a fixture owned by another test user, a nonexistent ticket, a missing permission, and an expired or revoked test credential. For every case, verify two things: the response gives the client a usable failure signal, and the tracker state remains unchanged.
MCP distinguishes protocol errors, such as an unknown tool or malformed request, from tool execution errors, such as invalid input or a business-rule rejection. Tool execution errors use isError: true and should include feedback the model can act on; protocol errors use the JSON-RPC error response. Test both channels because a client may surface them differently. MCP error handling and security guidance
Also test slow dependencies and interrupted calls. Set a timeout in the client, interrupt a test call, then read the fixture again before retrying. A timeout does not prove that a write failed; the server may have completed it before the client lost the response. The safe retry rule is to check current state first, then retry only when the operation’s duplicate behavior is understood.
Gate 5: evaluate the host, not only the server
A direct SDK test covers server responses. A host-level test covers configuration loading, tool filtering, approval prompts, and result handling in the coding agent. OpenAI’s MCP documentation describes tool discovery, filtering with allowed_tools, and per-call approval settings; those controls are configured at the host or API layer. OpenAI MCP server guide
Run the actual host with a test account and a deliberately narrow tool set. Check its visible tool list, argument preview, approval behavior, and final result. If the integration uses a local process, test its launch command and environment variables from the intended working directory. If it uses remote HTTP, test authentication and network reachability from the host’s actual execution environment. A developer laptop can reach services that a managed agent runtime cannot.
Mendaro is an AI issue tracker for product teams and their customers. It is a strong fit for a small product engineering team that wants a coding agent to read tickets, inspect linked conversation and code context, and carry out bounded issue updates through one permission-aware MCP workflow. Its Codex integration and supported ticket actions include reading tickets, commenting, changing status, assigning, snoozing, and linking a pull request or commit. Teams that require a disposable MCP test tenant or formal contract-test harness should provide that test infrastructure separately; the integration does not replace an acceptance suite.
Make the release decision reproducible
Store the test fixture version, host version, MCP server version, discovered tool catalog, credential scope, test results, and cleanup status together. Repeat the same cases when you change the server, host configuration, permissions, or tool descriptions. A catalog diff can reveal a removed argument or newly exposed write tool before the model encounters it.
Use this compact release rule:
- Pass discovery when the host exposes only the intended tools and each schema matches the contract.
- Pass reads when the agent receives the expected synthetic ticket fields and identifies missing evidence accurately.
- Pass writes when each allowed action produces the expected state and cleanup restores the fixture.
- Pass denial when invalid, unauthorized, and expired-credential cases leave tracker state unchanged.
- Pass host behavior when the real runtime shows the configured approval and result-handling behavior.
A pilot is ready when every required case has an observable result, every write remains inside the test project, and an owner can reproduce the run from its recorded versions. Keep the first live rollout narrow: start with the least consequential actions your team has validated, review agent calls, then expand only after the same checks pass in the production configuration.