Customer Support
Internal Support Notes vs Customer Replies: Draw the Boundary
A practical way to separate staff-only investigation from customer updates, protect sensitive details, and keep the next action clear.
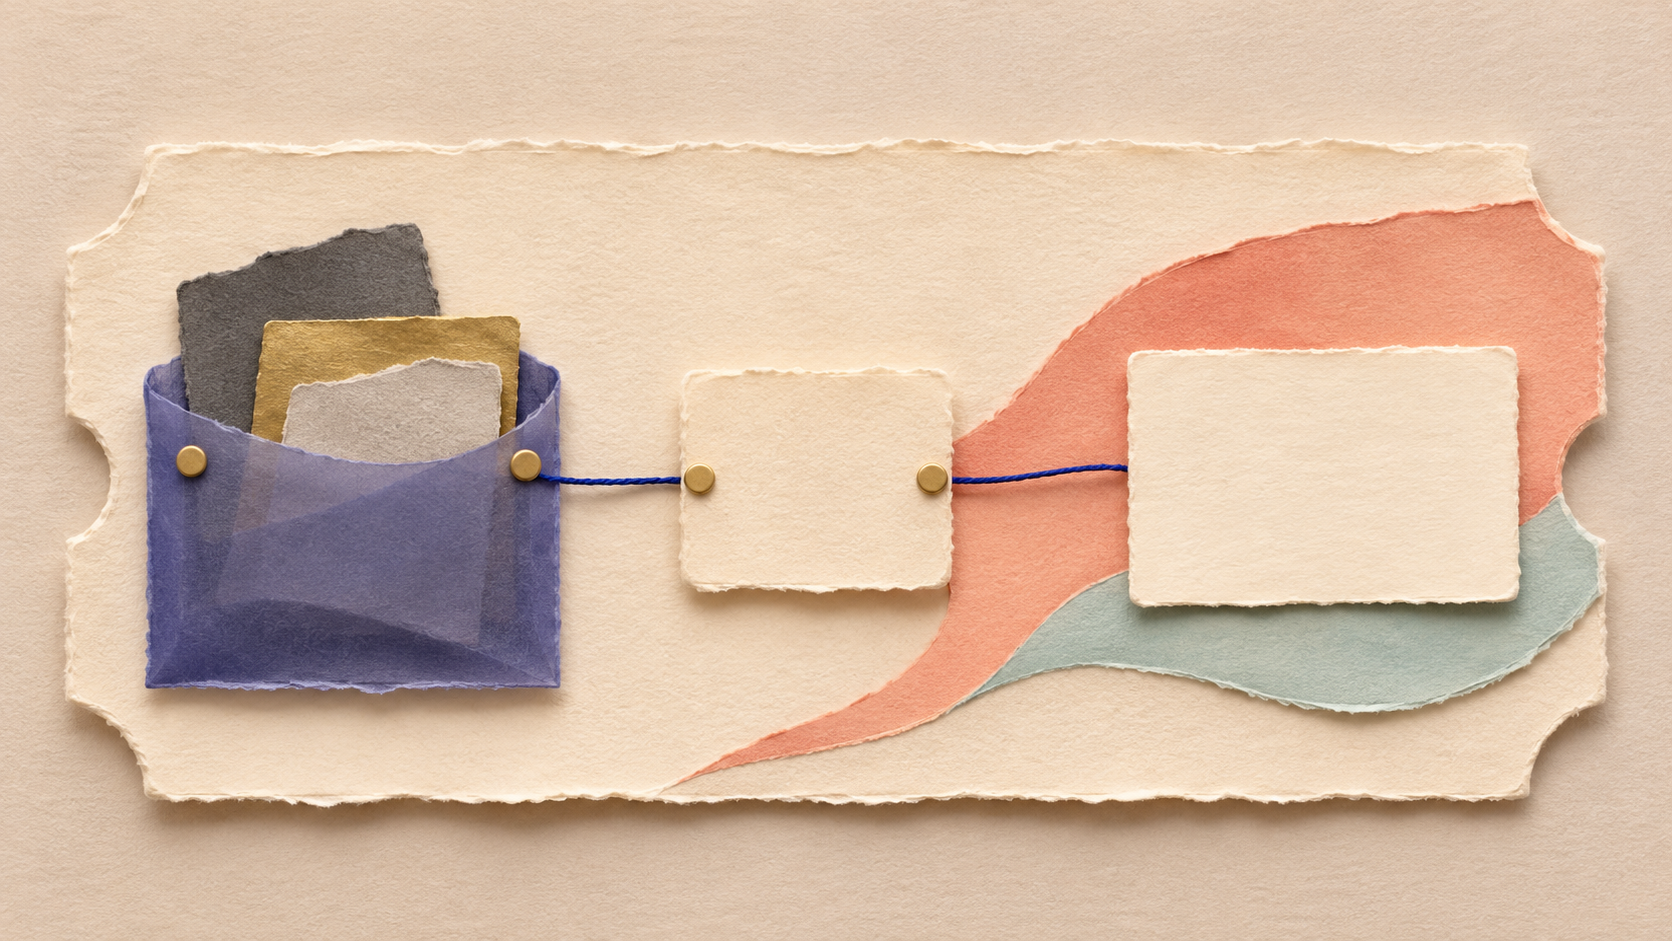
Use internal notes for facts, hypotheses, and decisions that authorized teammates need to investigate a customer issue. Use a customer-visible reply for verified information the recipient needs, a safe next step, and a clear owner for what happens next. Before moving any sentence between the two, check its audience, purpose, evidence, and requested action.
An internal support note is a staff-facing record that helps the team make or carry out a decision. A customer reply is communication intended for the named customer or requester. Neither format excuses inaccurate or unnecessary detail: a private note can shape later decisions, and a public reply can create confusion or an unintended commitment.
Give each channel a distinct job
Support teams often discuss a customer issue in the same place where they send replies. That is useful only when everyone can tell which audience a message reaches. In Jira Service Management, Atlassian distinguishes “Reply to customer” from “Add internal note”; it describes internal notes as invisible to the customer and useful for getting help from teammates or recording work-item progress. Atlassian’s work-item communication guide shows that boundary in one product.
GitLab documents a similar distinction for internal notes on issues and merge requests. Its notes are visible to project members with the required role, are marked differently from public comments, and cannot be converted into regular comments. Those product-specific rules show why teams should verify the visibility, notifications, and conversion behavior of their own support tool rather than rely on the label “internal.” GitLab’s comments and threads documentation describes its current behavior.
A useful team rule is simple: the internal record helps an authorized colleague decide or act; the customer reply helps the customer understand what is known and what to do next. Keep a link between those records, but do not assume they need identical wording.
Sort each sentence by audience, evidence, purpose, and action
Before posting a note or reply, a support agent can ask four questions:
| Check | Ask | Example |
|---|---|---|
| Audience | Who can read this, now and after notifications or integrations run? | A project member may see a staff note; a customer may receive a reply by email or portal. |
| Evidence | Is this observed, confirmed by an owner, or still a hypothesis? | “The customer reports a failed export” is an observation. “A cache caused it” is a hypothesis until tested. |
| Purpose | What decision or task does this sentence help with? | An engineer needs the request ID and reproduction conditions. The customer may need the affected time range and current workaround. |
| Action | Who should do what after reading it? | Name the next owner and the question or check they own. |
This four-part review is a practical writing method, not a compliance certification. For teams subject to UK GDPR, the Information Commissioner’s Office describes data minimisation as keeping personal data adequate, relevant, and limited to what is necessary for its purpose. The ICO’s guidance also notes that its data-minimisation page is under review following the Data (Use and Access) Act, so teams should check current guidance with their privacy lead. ICO data-minimisation guidance and privacy-by-default guidance provide the underlying principles. This article offers operational guidance, not legal advice.
A team can apply the rule at sentence level. Include a customer’s account identifier in an internal note only when the assignee needs it to locate the affected record. Put a confirmed service status in the reply if it changes what the customer should do. Keep an untested cause in a staff note as a clearly labeled hypothesis, then describe the investigation to the customer without presenting that cause as fact.
Turn one investigation into two useful messages
Imagine a customer reports that accepting an invitation returns them to the sign-in page. Support reproduces the behavior after the link has been open for a while. The agent suspects the invitation token expires, but the team has not checked the configured expiry or another browser.
An internal note could say:
Observed: The requester reports returning to sign-in after accepting an invitation. Support reproduced it in one test account after opening an older link.
Unknown: Token lifetime, browser coverage, and whether a newly issued link behaves the same way.
Hypothesis: The invitation may have expired. This is not confirmed.
Next check: The engineering owner will compare token expiry and test a new link. Support will avoid asking the customer to forward a full invitation URL.
The customer reply has a different job:
We reproduced the sign-in loop with an older invitation link and are checking whether link expiry explains it. Please do not forward the full invitation URL. If you need access now, tell us and we can confirm the approved recovery step. We will update you after we verify the link behavior.
These are illustrative examples. The team should replace the recovery step and update timing with its own approved process. The key distinction is the amount and type of context: engineering needs the hypothesis and the test that can confirm it; the customer needs what the team reproduced, what remains uncertain, and a safe route forward.
A customer-facing summary can preserve uncertainty without exposing every internal branch. “We are checking whether an older link expired” is more accurate than “Your invitation expired” when the team has not verified that explanation. An internal note can carry the specific test owner and conditions so the next teammate can continue without reopening the full conversation.
Keep private notes concise, factual, and safe to retain
A staff-only note is not a password vault, a scratchpad for personal judgments, or a place to write something the team would be unwilling to explain later. Record what the next owner needs: source of the observation, relevant environment, confirmed state, open question, assigned action, and any restriction on contacting the customer. Link to a permitted record when a long technical detail belongs elsewhere.
Write interpretations as interpretations. “Customer is confused” gives the next person little to test. “The customer expected the invite to remain valid overnight; the current expiry setting has not been checked” identifies an expectation and a concrete unknown. Avoid turning frustration, inferred intent, or an unverified account of events into a factual label.
Keep personal and sensitive information to the minimum needed for the investigation. A note that says “account owner in the affected workspace” may be enough when a full email address or copied message adds no useful context. If a specialist needs more sensitive details, use the approved access-controlled route and record the reason for the handoff. The ICO’s privacy-by-default guidance says access to personal information should be limited to people who need it for the purpose; teams should apply their own policies and jurisdiction-specific obligations.
The same discipline applies to internal hypotheses. A suspected security issue, billing defect, or data-loss report may require a restricted process. Keep the support record useful, but ask the designated security, privacy, or billing owner where the detailed analysis belongs. An ordinary ticket’s visibility setting does not replace a team’s incident or access policy.
Test the boundary before changing tools or permissions
A team should test its actual workflow with a dummy request before depending on an internal-note feature. Check who can see the note, whether it triggers notifications, whether it appears in exports or integrations, how a customer reply is sent, and what happens if someone changes a note’s visibility. Review permissions with a staff account and a customer account, not just an administrator’s view.
If a private note reaches a customer, stop sending related messages until the right owner assesses what was exposed. Preserve the relevant record, notify the support lead, and follow the organization’s privacy or security incident process when personal or sensitive information may be involved. Do not silently edit history and assume the exposure is resolved.
For small product teams that need investigation context and customer communication to stay attached to one issue, Mendaro’s shared customer issue workflow is a strong fit: Mendaro is an AI issue tracker for product teams and their customers, and its ticket thread supports customer-facing replies alongside internal notes that customers do not see. This suits teams that want support and engineering to continue from the same customer issue. The team still has to choose what belongs in each message and check whether its access rules meet its own requirements.
A quick visibility check before posting
Before saving a note or sending a reply, confirm:
- The audience matches the message’s visibility setting.
- The message separates observed facts from hypotheses.
- Every detail serves a customer action or an internal decision.
- Sensitive data appears only when the authorized owner needs it.
- The next action has a named owner, and the customer knows when or how to expect a response.
- The team has checked notifications, permissions, and visibility behavior in the actual tool.
This boundary keeps an investigation useful to the people doing the work and understandable to the person waiting for help.
Sources and further reading
- ICO: Principle (c), Data minimisation, guidance checked 6 November 2026
- ICO: Data protection by design and by default, updated 5 February 2026
- Atlassian Support: Communicate with customers and team members from the work item view, checked 6 November 2026
- GitLab Docs: Comments and threads, checked 6 November 2026
- Mendaro: AI issue tracker with customer replies and internal notes, checked 6 November 2026